
Assess
Evaluate existing cybersecurity controls, governance practices, risks, and organizational capabilities.
Cybersecurity|Governance|Risk|Compliance
Serenport helps CIOs, CISOs, and business leaders assess cybersecurity maturity, manage enterprise risk, and operationalize compliance with NIST CSF 2.0 and leading industry frameworks.
Assess. Prioritize. Improve.
Prepare, implement, and maintain continuous compliance.
Build a certified, resilient security management system.
Turn your compliance platform into an operational security governance program.
Strategic cybersecurity leadership for CIOs, CISOs, and governance teams.
Risk registers, vendor assessments, and board-ready reporting.
NIST CSF 2.0 Maturity Assessment & Advisory
Serenport helps organizations evaluate their current cybersecurity capabilities, establish realistic maturity objectives, and implement structured improvement programs aligned with the NIST Cybersecurity Framework (CSF) 2.0.
Our assessment covers your existing cybersecurity governance, policies, processes, and technical controls across all six CSF functions: Govern, Identify, Protect, Detect, Respond, and Recover. Working with your leadership and security teams, we establish an evidence-based Current Profile, define an achievable Target Profile, and develop a prioritized improvement roadmap.
Hover or tap a function to see what we assess.
Our approach
A maturity score is only the starting point. We connect every gap to an accountable owner, a funded action, and a milestone your leadership can track.
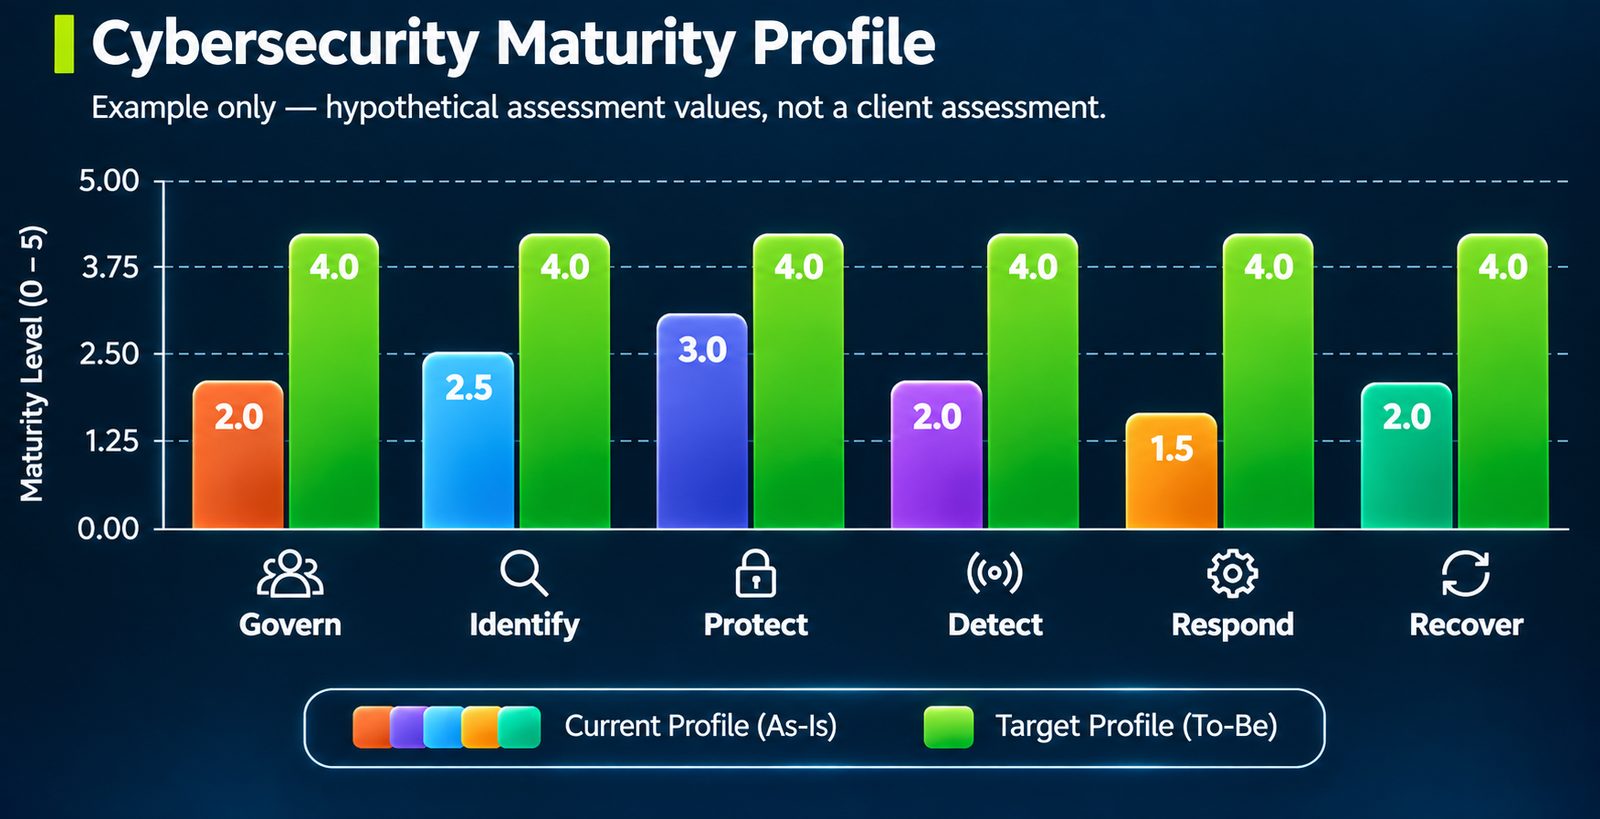
Evaluate existing cybersecurity controls, governance practices, risks, and organizational capabilities.
Establish target maturity objectives, success criteria, responsibilities, and realistic implementation timelines.
Create a Plan of Action and Milestones that identifies control deficiencies, remediation activities, accountable owners, resources, and target completion dates.
Provide advisory support during remediation, track milestones, validate progress, and report results to executive leadership.
Establish ongoing governance, performance indicators, periodic reassessments, and continuous improvement practices.
Our goal is to help your organization reduce cybersecurity risk, strengthen governance, improve resilience, and demonstrate progress toward applicable compliance obligations.
NIST CSF alignment alone does not establish regulatory compliance or guarantee certification. Serenport helps organizations understand and address the specific requirements relevant to their operations.
Partner with Serenport to turn cybersecurity assessment findings into measurable improvements.
Services
Engage us for a single assessment or as an ongoing extension of your security leadership team.
An independent, evidence-based view of your security program and a roadmap leadership can act on.
Prepare for Type I and Type II reports and stay audit-ready year-round, not just in audit season.
Design and implement an ISMS aligned to ISO/IEC 27001:2022 and guide you through certification.
Configure and optimize your compliance automation platform so it drives real governance, not just dashboards.
Experienced security leadership on a flexible basis for organizations that need strategy without a full-time hire.
Identify, quantify, and manage risk across your organization and supply chain.
Industries
State and city agencies, authorities, and their contractors.
NYS DFS Part 500, SOC 2, and examiner-ready programs.
HIPAA Security Rule risk analysis and safeguards.
Research data protection, FERPA, NIST 800-171, and GLBA.
SOC 2 and ISO 27001 to unblock enterprise sales.
Right-sized security governance for donor and program data.
OT/IT risk and supply-chain security requirements.
Client-driven security questionnaires and attestations.
Government (MWBE)
Serenport is certified as a Minority- and Women-owned Business Enterprise by both New York State and New York City. Agencies and prime contractors can engage us to strengthen cybersecurity programs while meeting MWBE utilization goals.
Serenport is led by Oneil Hinds, PhD, MPA, CRISC, CISM, CISA, PMP. His graduate training in public administration brings a working understanding of agency governance, budgeting, procurement, and public accountability, so our cybersecurity recommendations fit how government actually operates.
Insights
Why CSF 2.0 makes cybersecurity governance an executive responsibility, and how to report on it.
Getting beyond green dashboards: connecting automated evidence to real risk decisions.
Title IV institutions are financial institutions under federal law. What the FTC Safeguards Rule requires, the 24-hour breach clock, and how FERPA fits.
Schedule a complimentary 30-minute consultation to discuss your compliance goals, risk posture, and priorities.